


Latest Microsoft MS-102 Practice Test Questions, Microsoft 365 Administrator Exam Dumps
Apr-2026 Pass Microsoft MS-102 Exam in First Attempt Easily
NEW QUESTION # 226
You have a Microsoft 365 ES subscription.
From the Microsoft 365 Defender portal, you review your company's Microsoft Secure Score.
You discover a large number of recommended actions.
You need to ensure that the actions can be filtered based on specific department names.
What should you create first?
- A. a dynamic security group
- B. a custom detection rule
- C. an administrative unit
- D. a tag
Answer: C
NEW QUESTION # 227
Your network contains an Active Directory domain and an Azure AD tenant.
You implement directory synchronization for all 10.000 users in the organization.
You automate the creation of 100 new user accounts.
You need to ensure that the new user accounts synchronize to Azure AD as quickly as possible.
Which command should you run? To answer, select the appropriate options in the answer area.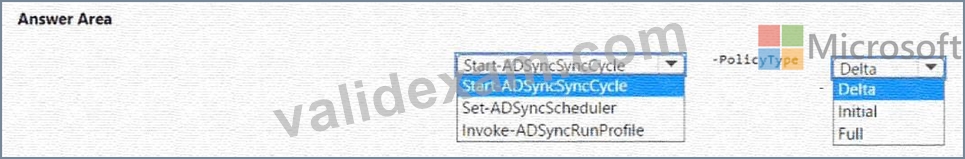
Answer:
Explanation: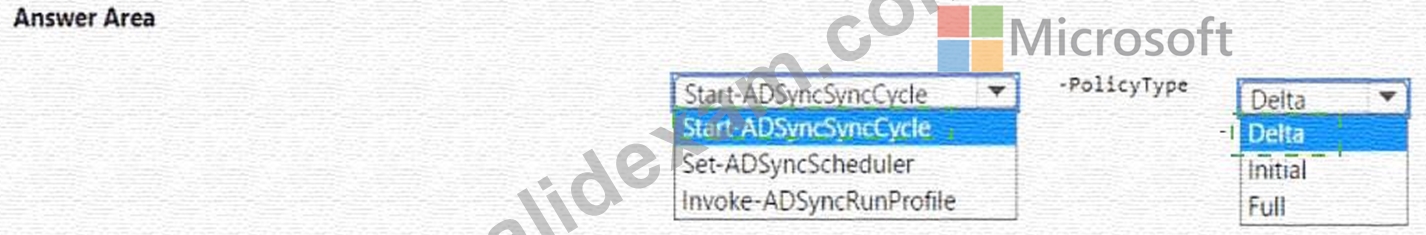
Explanation:
NEW QUESTION # 228
You have a Microsoft 365 tenant that contains the groups shown in the following table.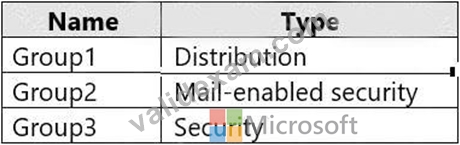
You plan to create a new Windows 10 Security Baseline profile.
To which groups can you assign to the profile?
- A. Group1. Group2. and Group3
- B. Group2 and Group3 only
- C. Group1 and Group3 only
- D. Group3 only
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/protect/security-baselines-configure#create-the-profile
https://docs.microsoft.com/en-us/microsoft-365/admin/create-groups/compare-groups?view=o365-worldwide
NEW QUESTION # 229
You have a Microsoft 365 Enterprise E5 subscription.
You add a cloud-based app named App1 to the Azure AD enterprise applications list.
You need to ensure that two-step verification is enforced for all user accounts the next time they connect to App1.
Which three settings should you configure from the policy? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.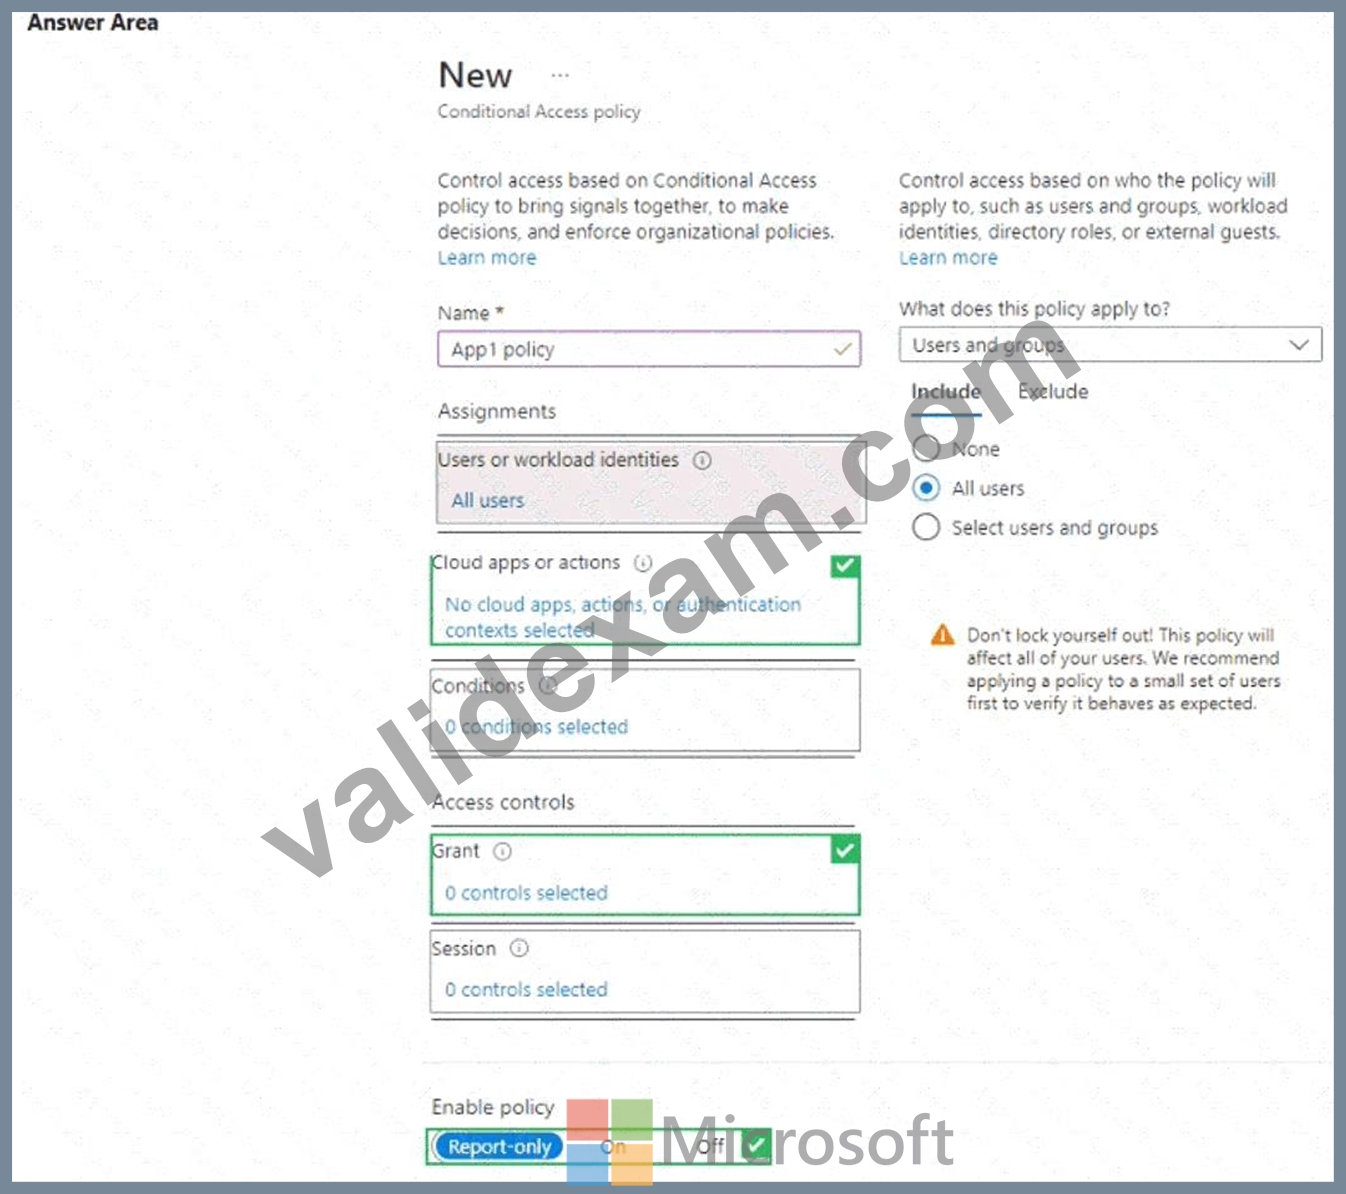
Answer:
Explanation: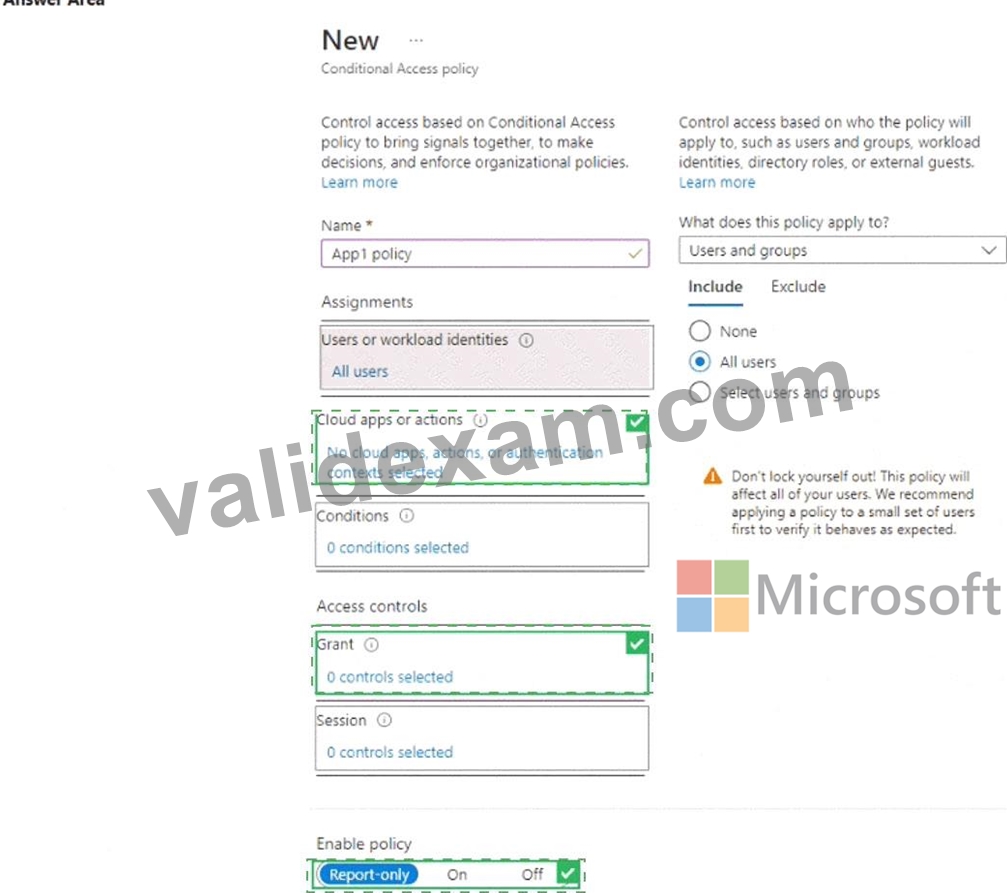
Explanation:
NEW QUESTION # 230
You have a Microsoft 365 E5 subscription and use Microsoft Defender for Cloud Apps.
You need to configure Cloud Discovery to generate a report that identifies top potential risks and provides a workflow to mitigate and manage the risks.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.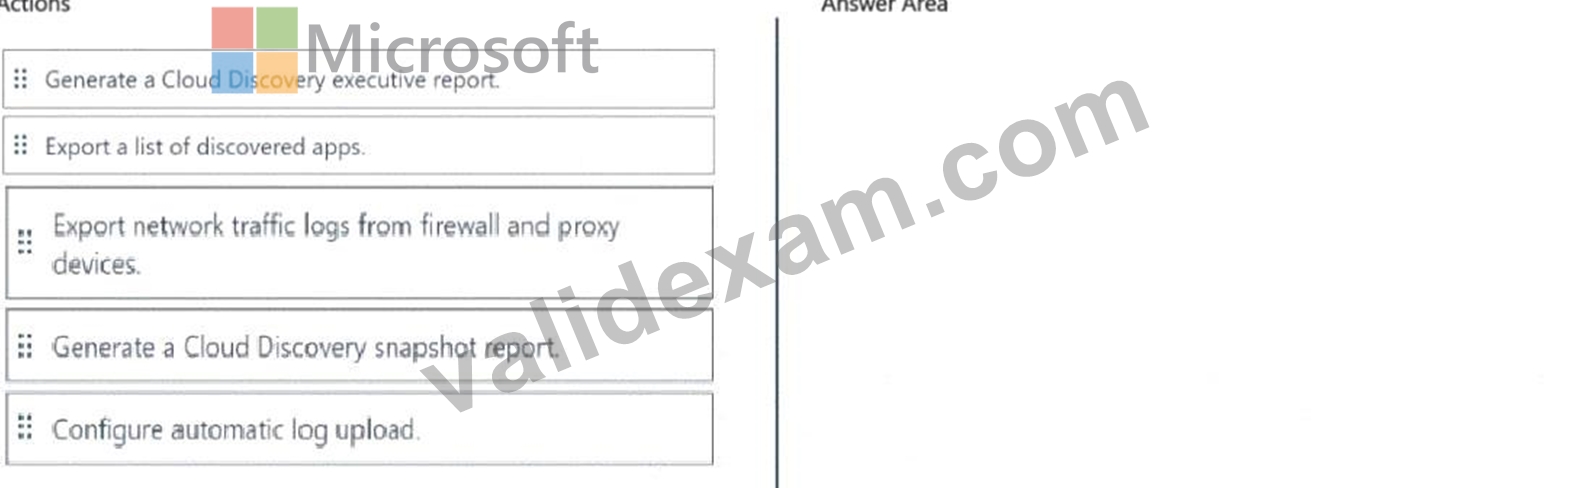
Answer:
Explanation: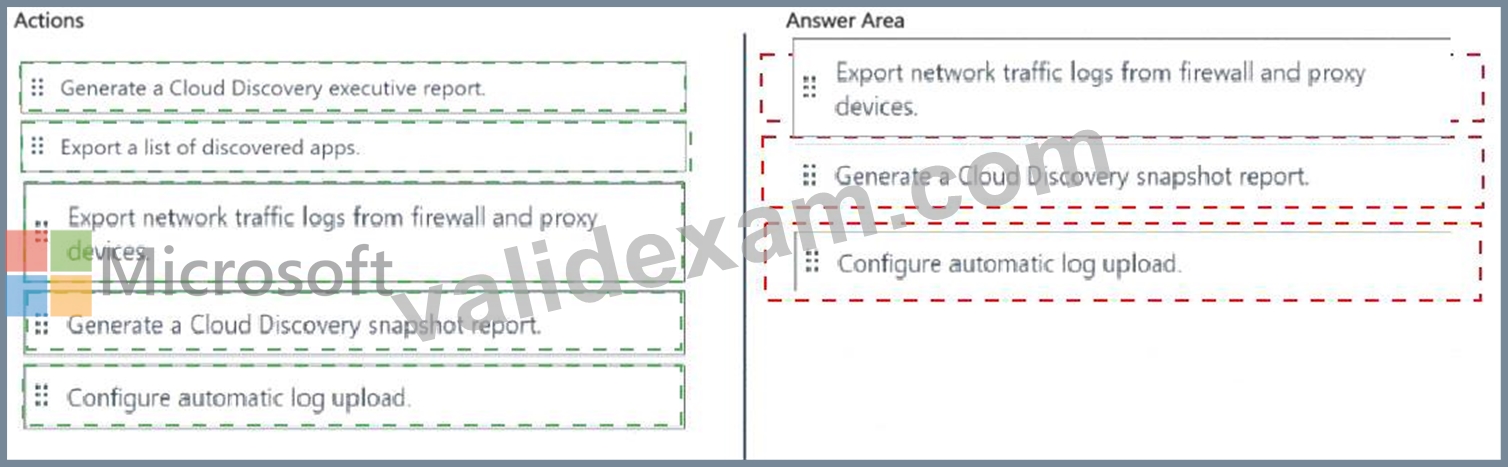
Explanation: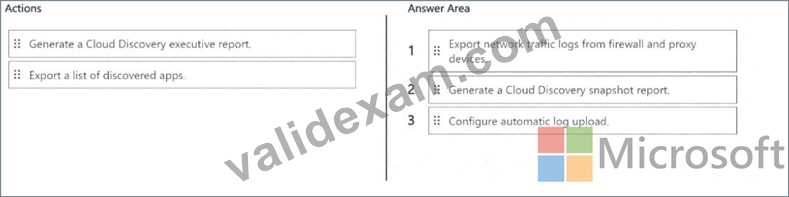
NEW QUESTION # 231
HOTSPOT
You have a Microsoft 365 subscription that contains a Microsoft 365 group named Group1. Group1 is configured as shown in the following exhibit.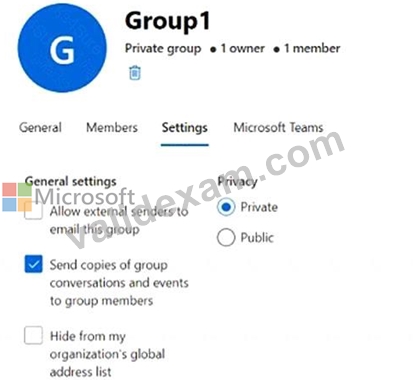
An external user named User1 has an email address of [email protected].
You need to add User1 to Group1.
What should you do first, and which portal should you use? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.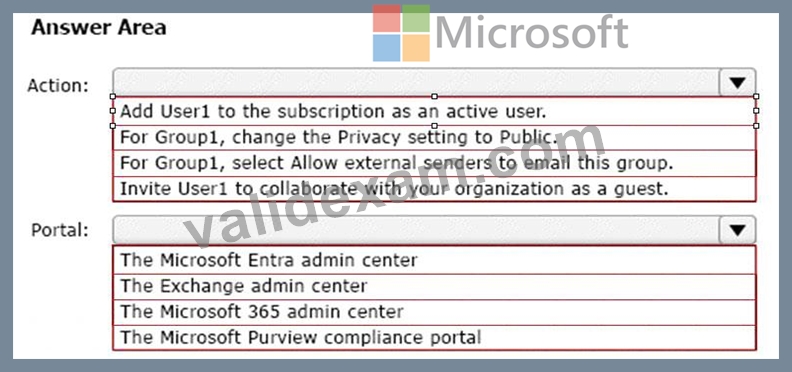
Answer:
Explanation: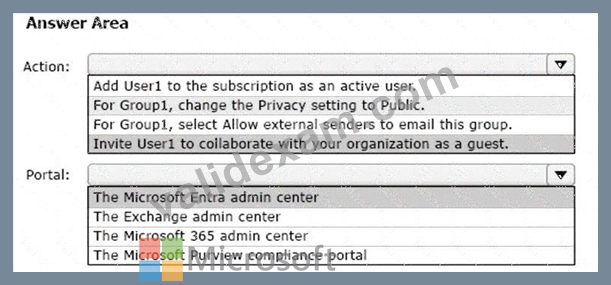
Box 1: Invite User1 to collaborate with your organization as a guest.
To manage guest users of a Microsoft 365 tenant via the Admin Center portal, go through the following steps.
Navigate with your Web browser to https://admin.microsoft.com.
On the left pane, click on "Users", then click "Guest Users".
On the "Guest Users" page, to create a new guest user, click on either the "Add a guest user" link on the top of the page or click on "Go to Azure Active Directory to add guest users" link at the bottom of the page. Both of these links will take you to the Azure Active Directory portal, which is located at https://aad.portal.azure.com.
On the "New user" page in the Microsoft Azure portal, you must choose to either "Create user" or "Invite user". If you choose the "Create user" option, this will create a new user in your organization, which will have a login address with format username@tenantdomain,dot,com. If you choose the "Invite user" option, this will invite a new guest user to collaborate with your organization. The user will be emailed an email invitation which they can accept in order to begin collaborating. For the purpose of creating a guest user, you must choose the "Invite user" option.
Box 2: The Microsoft Entra admin center
Microsoft Entra admin center unites Azure AD with family of identity and access products Microsoft Entra admin center gives customers an entire toolset to secure access for everyone and everything in multicloud and multiplatform environments. The entire Microsoft Entra product family is available at this new admin center, including Azure Active Directory (Azure AD) and Microsoft Entra Permissions Management, formerly known as CloudKnox.
Starting this month, waves of customers will begin to be automatically directed to entra.microsoft.com from Microsoft 365 in place of the Azure AD admin center (aad.portal.azure.com).
Reference:
https://stefanos.cloud/kb/how-to-manage-microsoft-365-guest-users
https://m365admin.handsontek.net/microsoft-entra-admin-center-unites-azure-ad-with-family-of-identity-and-acc
NEW QUESTION # 232
You have a Microsoft 365 E5 tenant that contains four devices enrolled in Microsoft Intune as shown in the following table.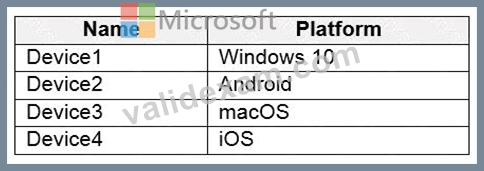
You plan to deploy Microsoft 365 Apps for enterprise by using Microsoft Endpoint Manager.
To which devices can you deploy Microsoft 365 Apps for enterprise?
- A. Device1 only
- B. Device1 and Device3 only
- C. Device2 and Device4 only
- D. Device1, Device2. and Device3 only
- E. Device1, Device2, Device3, and Device4
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/apps/apps-add
NEW QUESTION # 233
You have a Microsoft 365 E5 subscription.
You need to configure Microsoft Defender for Office 365 to meet the following requirements:
* A user's email sending patterns must be used to minimize false positives for spoof protection.
* Documents uploaded to Microsoft Teams, SharePoint Online, and OneDrive must be protected by using Defender for Office 365.
What should you configure for each requirement? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.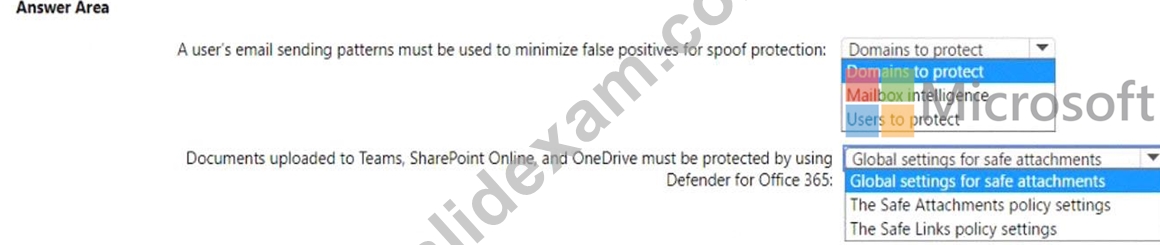
Answer:
Explanation: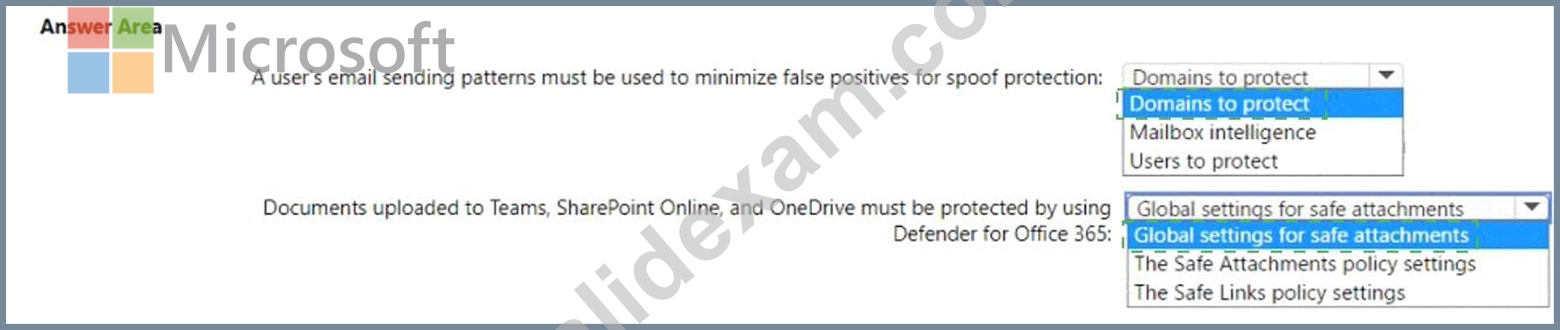
Explanation: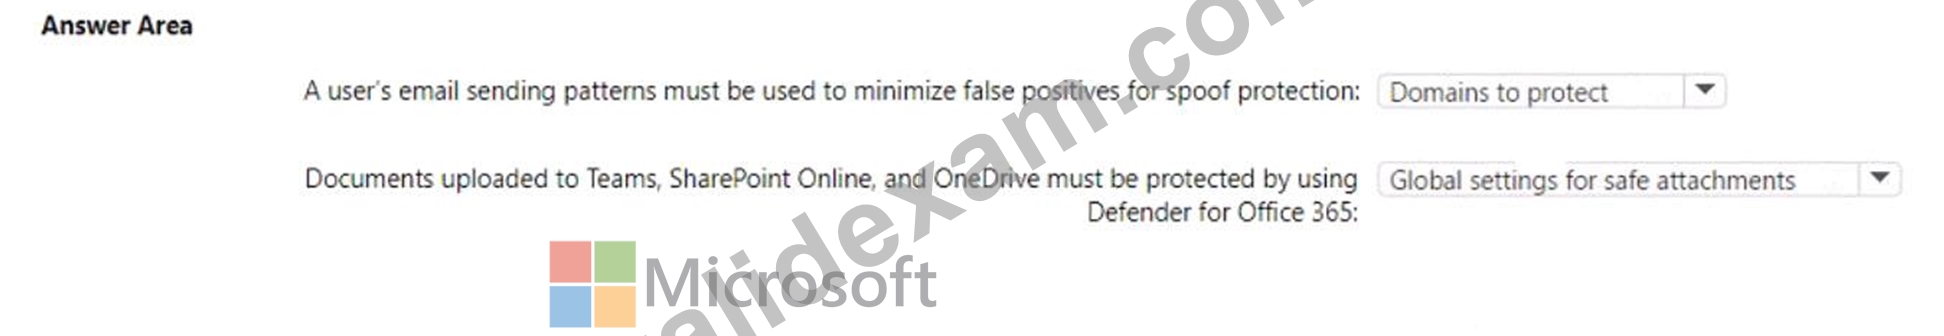
NEW QUESTION # 234
Your network contains an Active Directory domain and an Azure AD tenant.
You implement directory synchronization for all 10.000 users in the organization.
You automate the creation of 100 new user accounts.
You need to ensure that the new user accounts synchronize to Azure AD as quickly as possible.
Which command should you run? To answer, select the appropriate options in the answer area.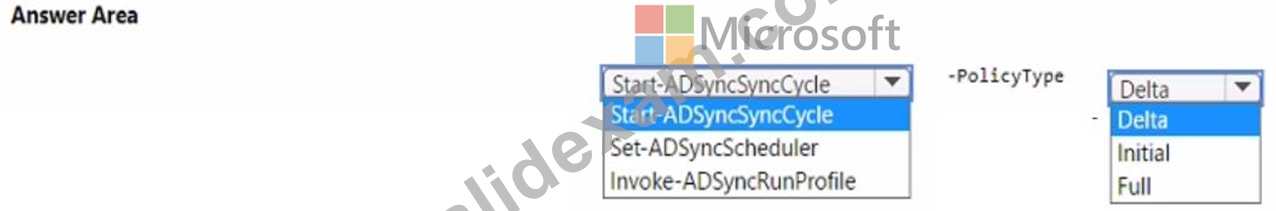
Answer:
Explanation: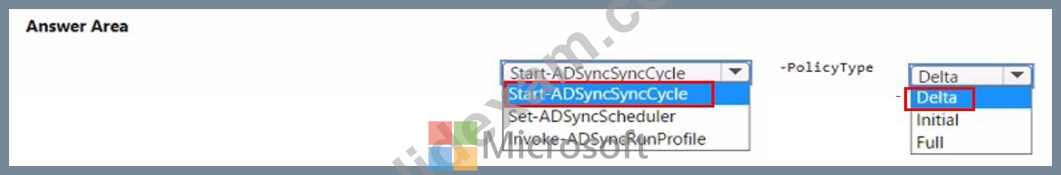
NEW QUESTION # 235
You have a Microsoft 365 subscription that contains the users in the following table.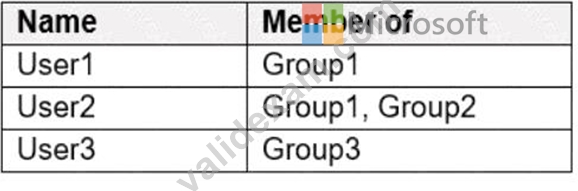
In Microsoft Endpoint Manager, you create two device type restrictions that have the settings shown in the following table.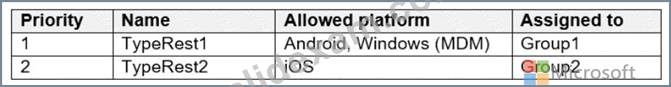
In Microsoft Endpoint Manager, you create three device limit restrictions that have the settings shown in the following table.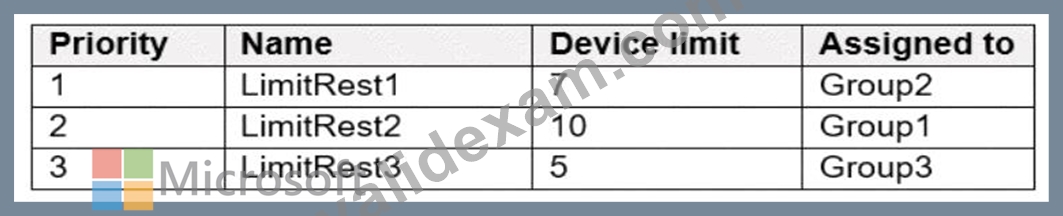
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.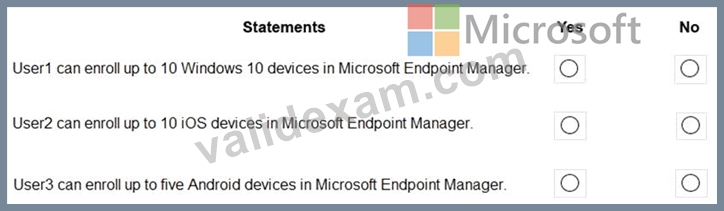
Answer:
Explanation: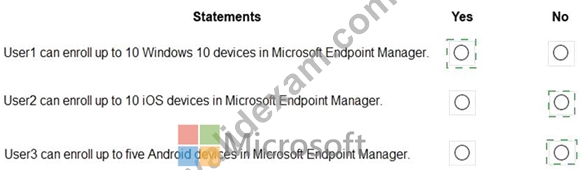
Explanation: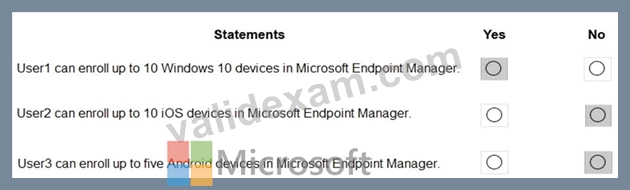
NEW QUESTION # 236
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint site named Sitel. You need to perform the following tasks:
* Create a sensitive info type named SIT1 based on a regular expression.
* Add a watermark to all new documents that are matched by SIT1.
Which two settings should you use in the Microsoft Purview compliance portal? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.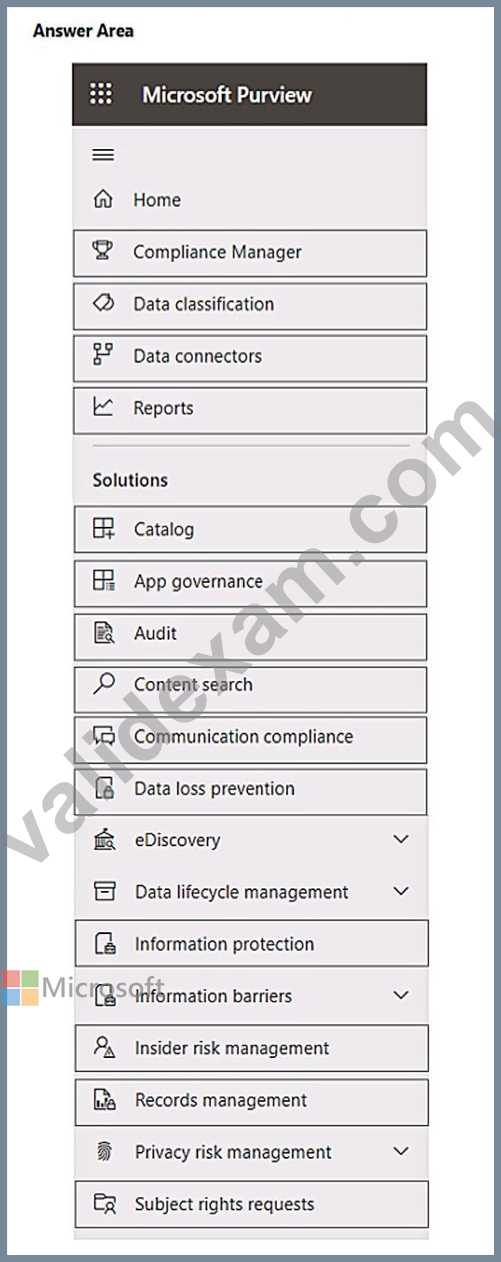
Answer:
Explanation: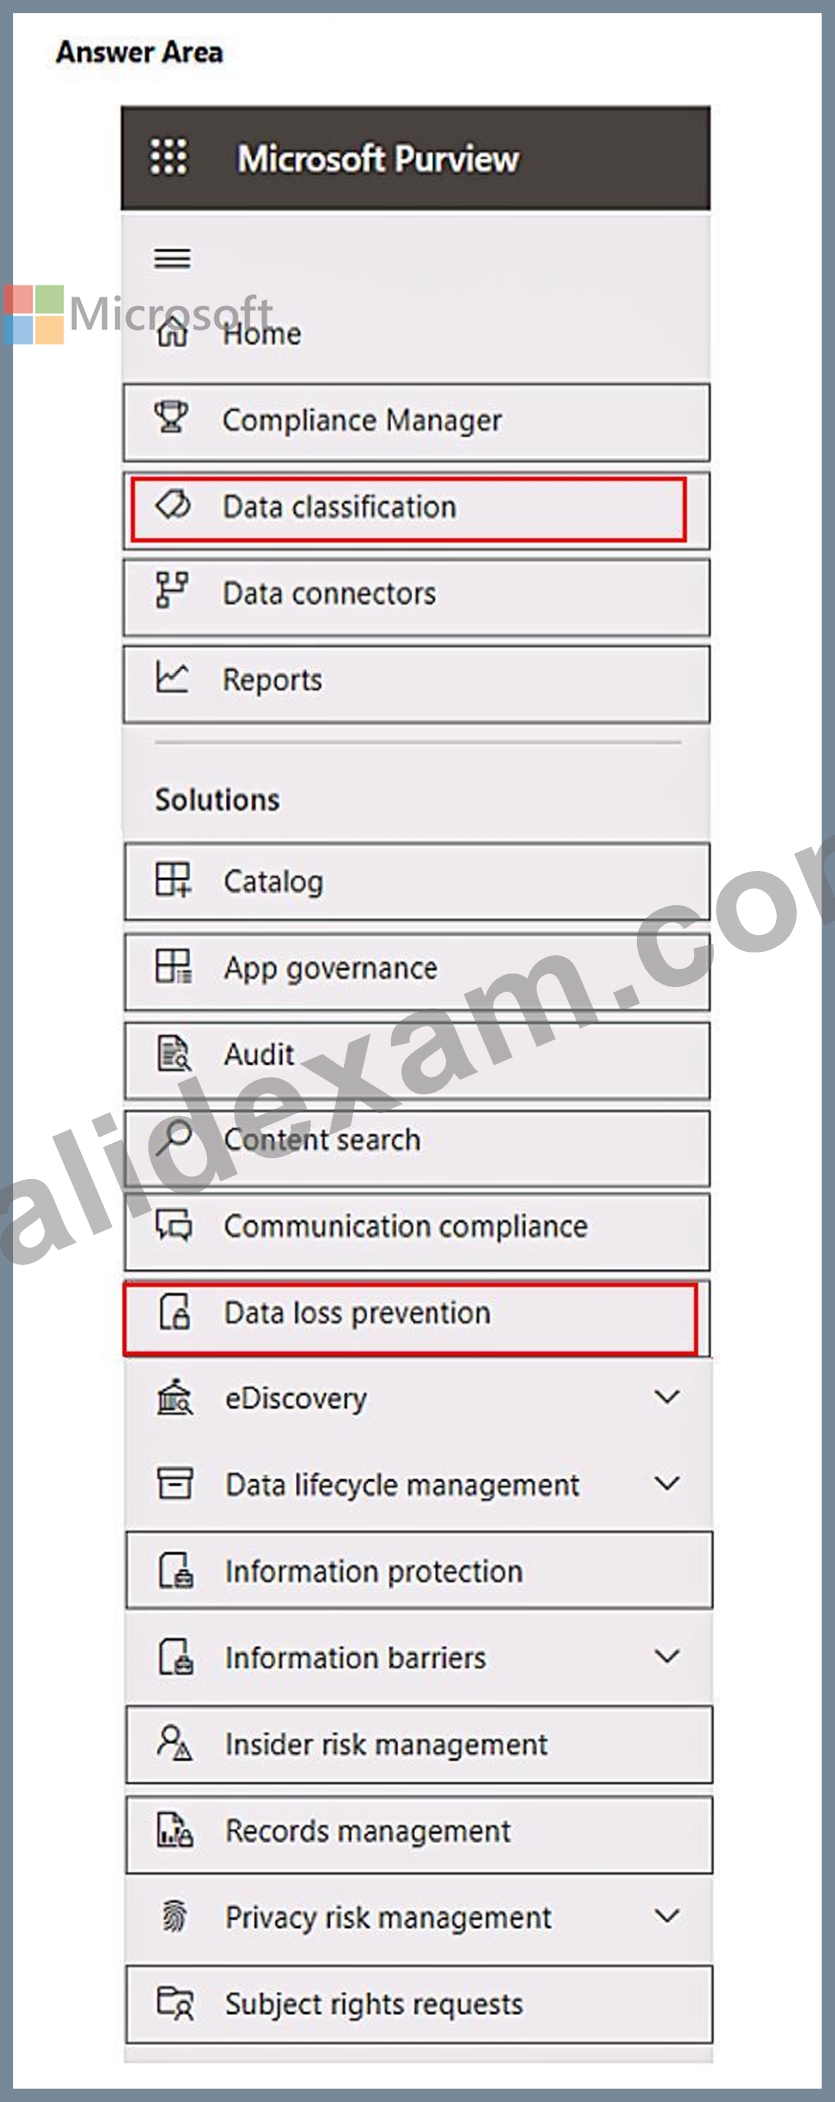
NEW QUESTION # 237
Your network contains an on-premises Active Directory domain. You have a Microsoft 365 subscription.
You implement a directory synchronization solution that uses pass-through authentication.
You configure Microsoft Entra Password protection as shown in the following exhibit.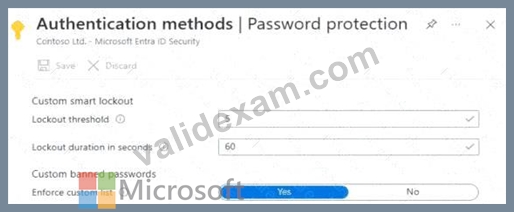
You discover that Active Directory users can use the passwords in the custom banned passwords list.
You need to ensure that banned passwords are banned for all users.
Which three actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point.
- A. From a domain controller, install the Microsoft Entra Application Proxy connector.
- B. From Custom banned passwords, modify the Enforce custom list setting.
- C. From a domain controller, install the Microsoft Entra Password Protection Proxy.
- D. From all the domain controllers, install the Microsoft Entra Password Protection DC Agent.
- E. From Password protection for Windows Server Active Directory, modify the Mode setting.
- F. From Active Directory, modify the Default Domain Policy.
Answer: C,D,E
NEW QUESTION # 238
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.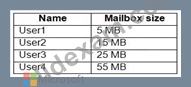
You have a Microsoft Office 365 retention label named Retention1 that is published to Exchange email.
You have a Microsoft Exchange Online retention policy that is applied to all mailboxes. The retention policy contains a retention tag named Retention2.
Which users can assign Retention1 and Retention2 to their emails? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.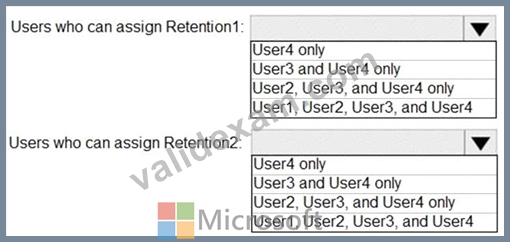
Answer:
Explanation: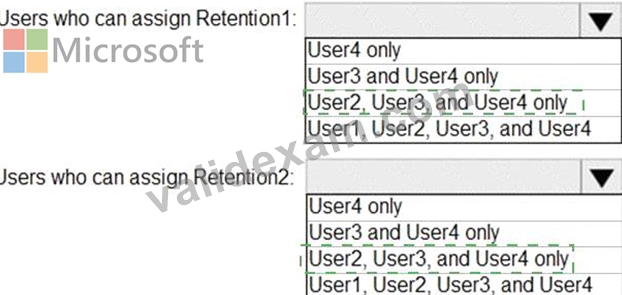
Explanation
Graphical user interface, text, application, chat or text message Description automatically generated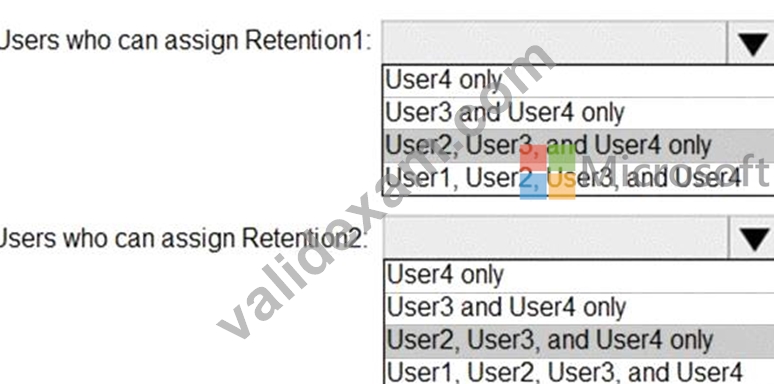
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention-policies-exchange?view=o365-worldwide
NEW QUESTION # 239
You need to meet the technical requirements and planned changes for Intune.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.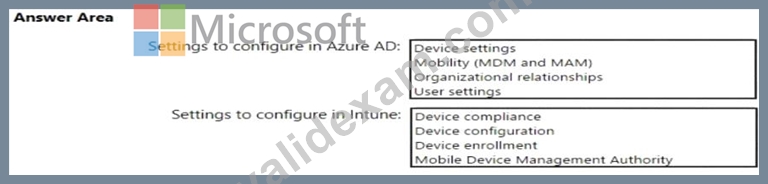
Answer:
Explanation: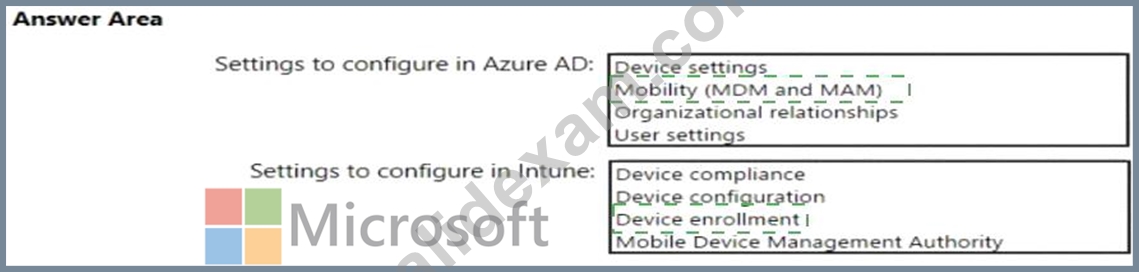
Explanation: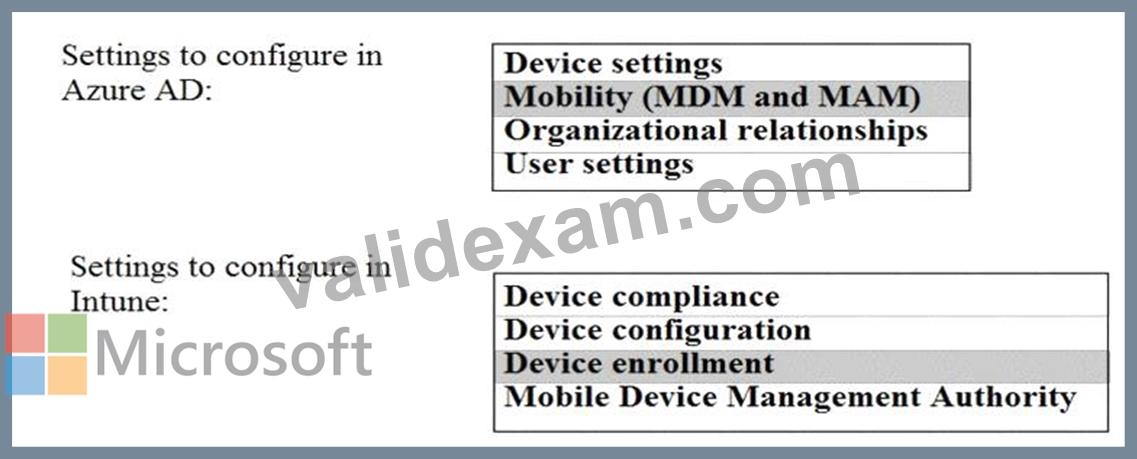
Reference:
https://docs.microsoft.com/en-us/intune/windows-enroll
Topic 1, Contoso, Ltd
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
The company has the employees and devices shown in the following table.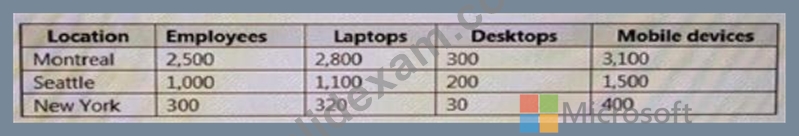
Contoso recently purchased a Microsoft 365 ES subscription.
Existing Environment
Requirement
The network contains an on-premises Active Directory forest named contoso.com. The forest contains the servers shown in the following table.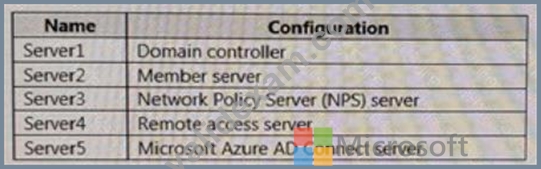
All servers run Windows Server 2016. All desktops and laptops are Windows 10 Enterprise and are joined to the domain.
The mobile devices of the users in the Montreal and Seattle offices run Android. The mobile devices of the users in the New York office run iOS.
The domain is synced to Azure Active Directory (Azure AD) and includes the users shown in the following table.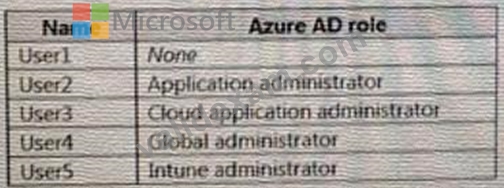
The domain also includes a group named Group1.
Planned Changes
Contoso plans to implement the following changes:
*Implement Microsoft 365.
*Manage devices by using Microsoft Intune.
*Implement Azure Advanced Threat Protection (ATP).
*Every September, apply the latest feature updates to all Windows computers. Every March, apply the latest feature updates to the computers in the New York office only.
Technical Requirements
Contoso identifies the following technical requirements:
*When a Windows 10 device is joined to Azure AD, the device must enroll in Intune automaticity.
*Dedicated support technicians must enroll all the Montreal office mobile devices in Intune.
*User1 must be able to enroll all the New York office mobile devices in Intune.
*Azure ATP sensors must be installed and must NOT use port mirroring.
*Whenever possible, the principle of least privilege must be used.
*A Microsoft Store for Business must be created.
Compliance Requirements
Contoso identifies the following compliance requirements:
*Ensure that the users in Group1 can only access Microsoft Exchange Online from devices that are enrolled in Intune and configured in accordance with the corporate policy.
*Configure Windows Information Protection (W1P) for the Windows 10 devices.
NEW QUESTION # 240
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site1.
You need to automatically label the documents on Site1 that contain credit card numbers.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.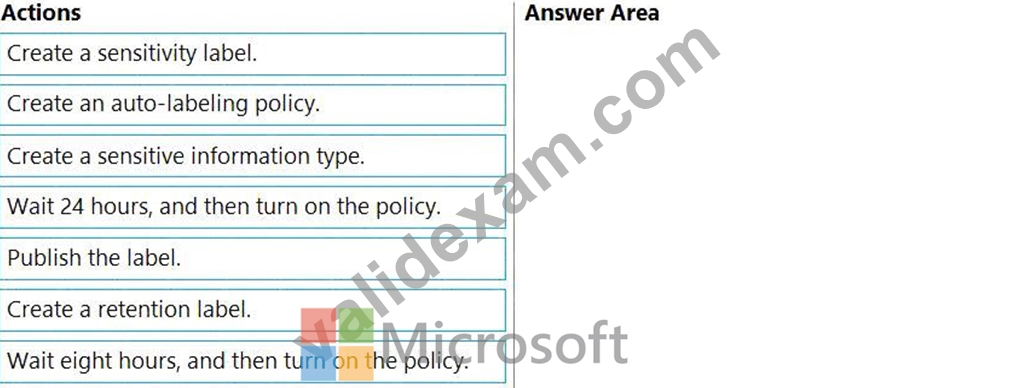
Answer:
Explanation: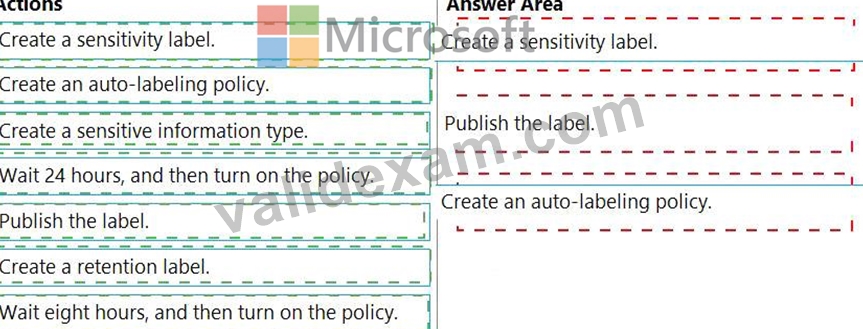
Explanation: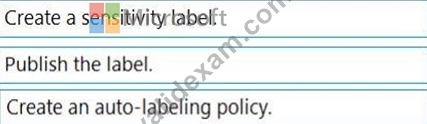
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide#what- label-policies-can-do
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365- worldwide
NEW QUESTION # 241
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint site named Sitel. You need to perform the following tasks:
* Create a sensitive info type named SIT1 based on a regular expression.
* Add a watermark to all new documents that are matched by SIT1.
Which two settings should you use in the Microsoft Purview compliance portal? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.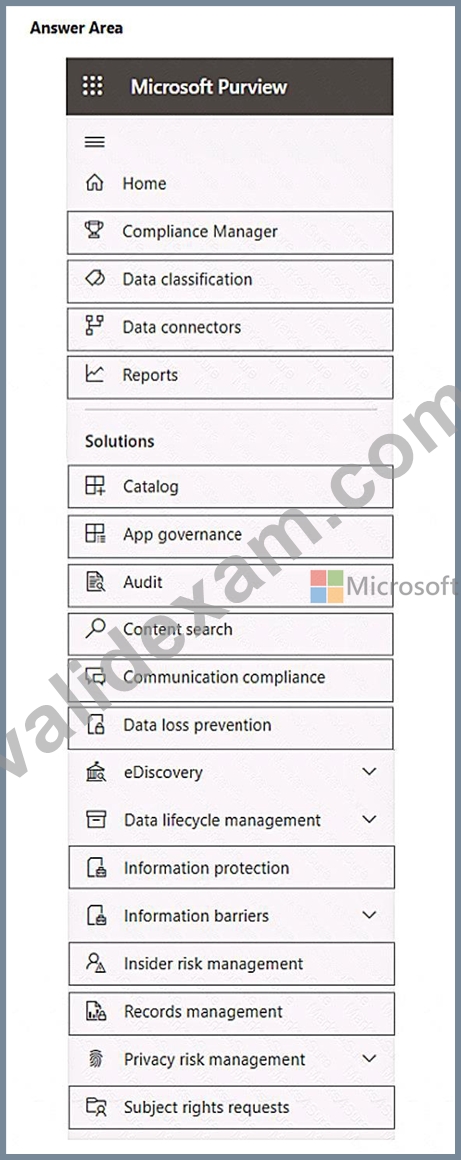
Answer:
Explanation: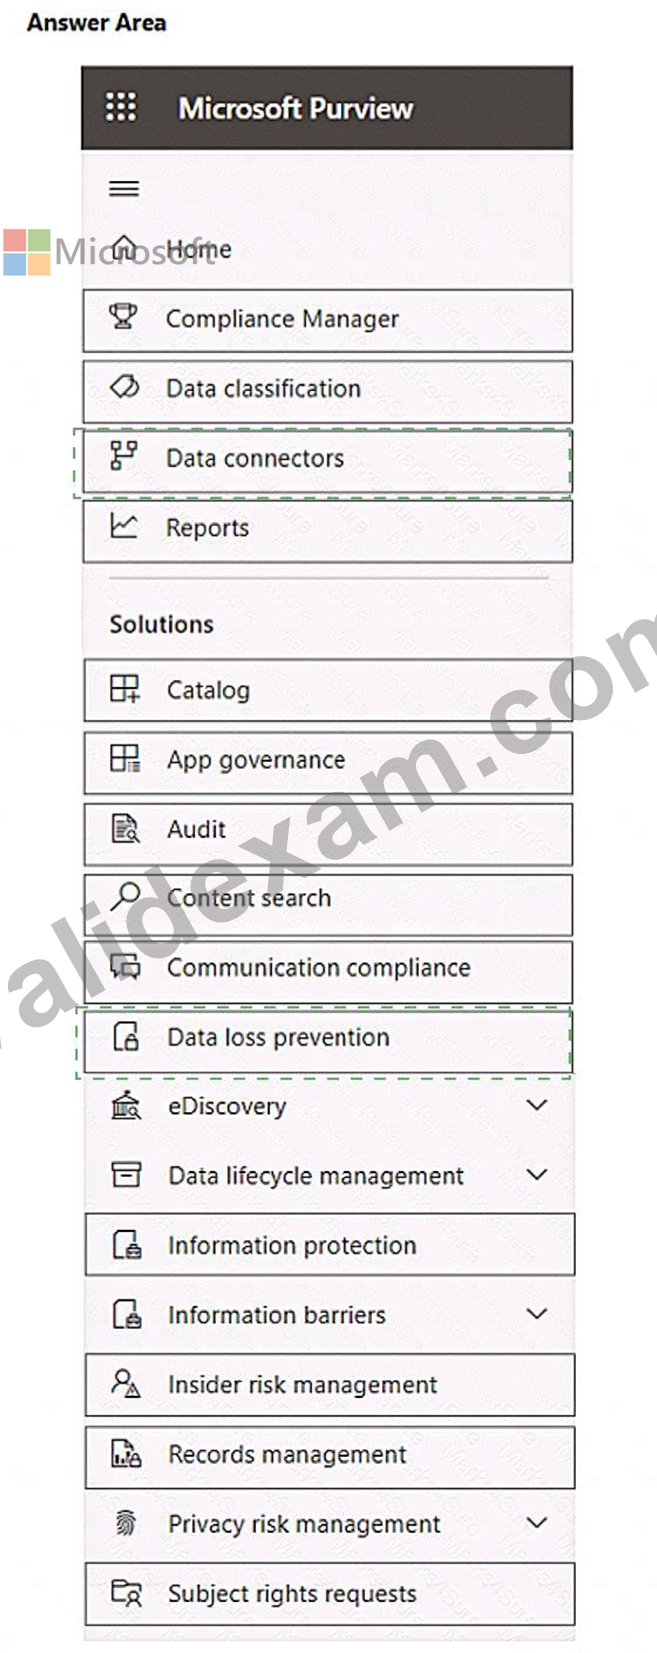
Explanation: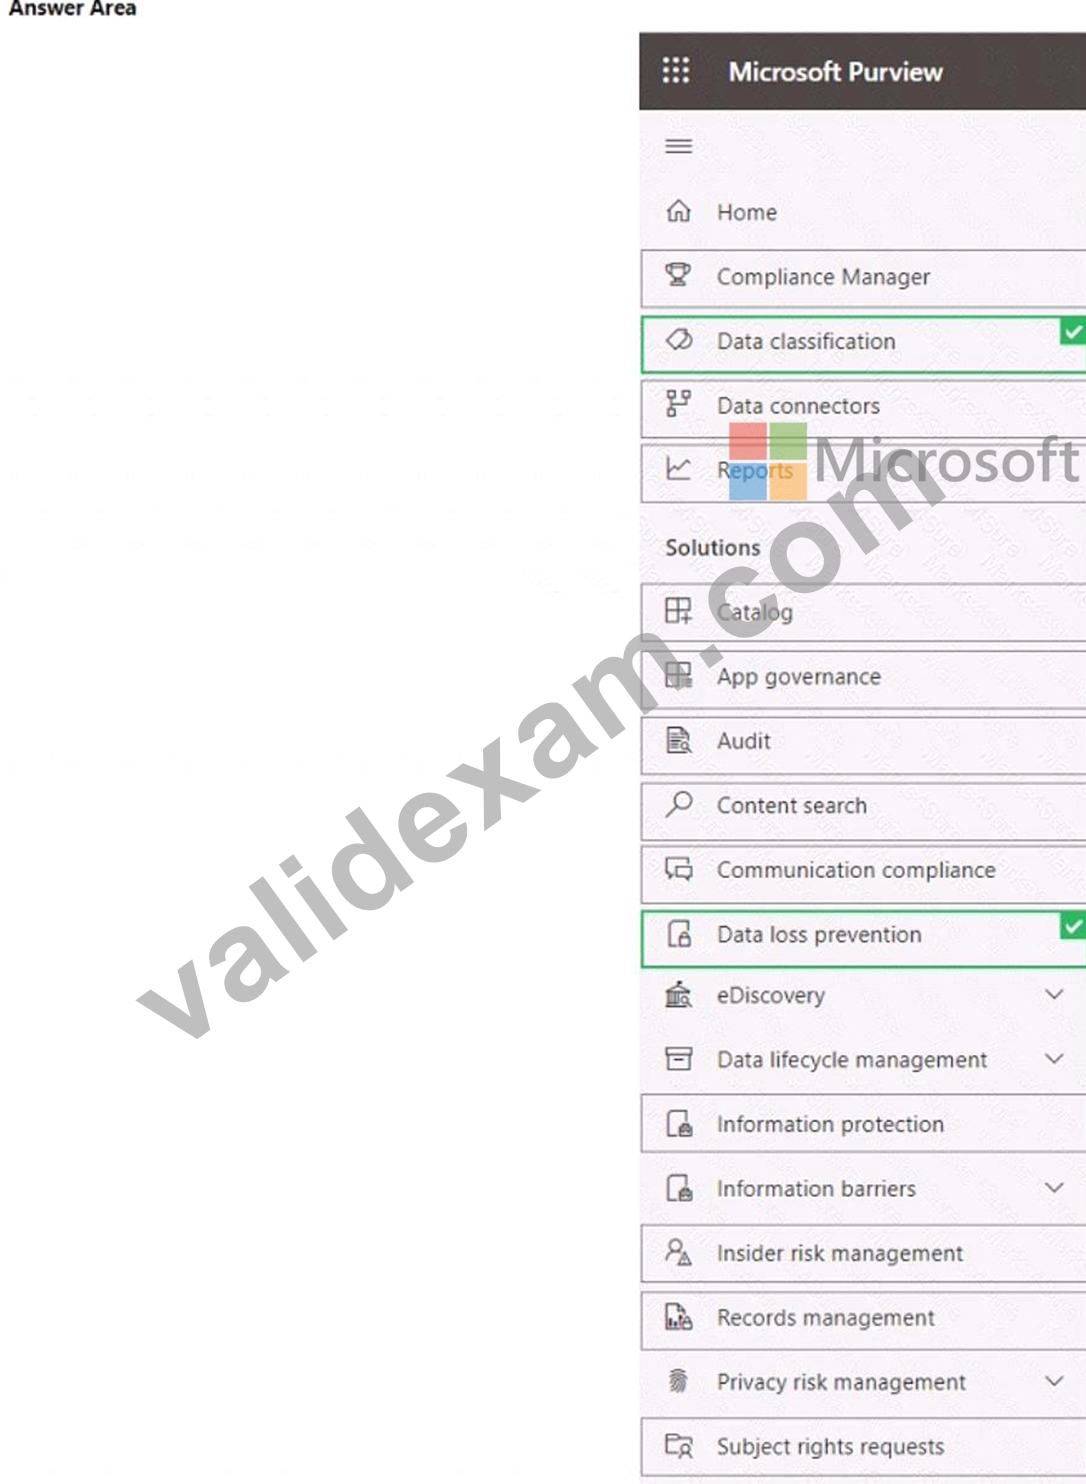
NEW QUESTION # 242
You have the sensitivity labels shown in the following exhibit.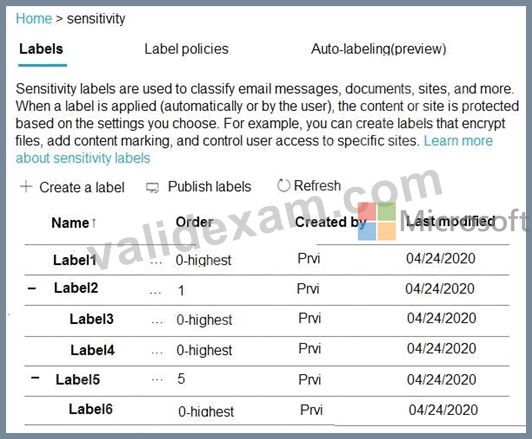
Which labels can users apply to content?
- A. Label1, Label3, Label4, and Label6 only
- B. Label1, Label2, and Label5 only
- C. Label3, Label4, and Label6 only
- D. Label1, Label2. Label3. Label4. Label5. and Label6
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide
NEW QUESTION # 243
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it As a result, these questions will not appear in the review screen.
Your network contains an on-premises Active Directory domain. The domain contains domain controllers that run Windows Server 2019. The functional level of the forest and the domain is Windows Server 2012 R2.
The domain contains 100 computers that run Windows 10 and a member server named Server1 that runs Windows Server 2012 R2.
You plan to use Server1 to manage the domain and to configure Windows 10 Group Policy settings.
You install the Group Policy Management Console (GPMC) on Server1.
You need to configure the Windows Update for Business Group Policy settings on Server1.
Solution: You raise the domain functional level to Windows Server 2019. You copy the Group Policy Administrative Templates from a Windows 10 computer to the Netlogon share on all the domain controllers.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION # 244
You have several devices enrolled in Microsoft Endpoint Manager.
You have a Microsoft Azure Active Directory (Azure AD) tenant that includes the users shown in the following table.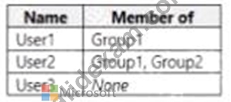
The device type restrictions in Endpoint Manager are configured as shown in the following table.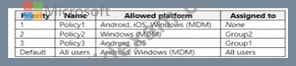
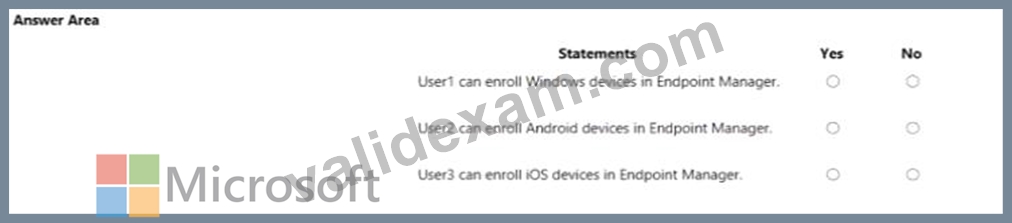
Answer:
Explanation: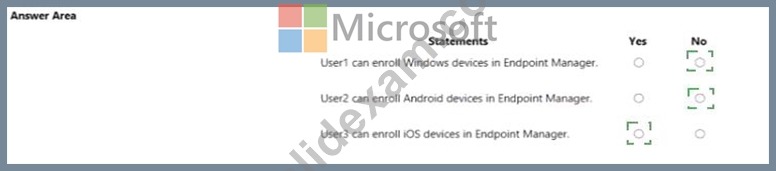
Explanation: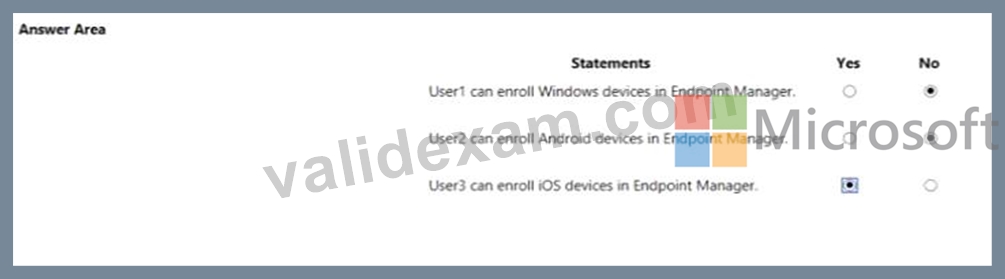
NEW QUESTION # 245
You have a Microsoft 365 tenant.
You plan to manage incidents in the tenant by using the Microsoft 365 security center.
Which Microsoft service source will appear on the Incidents page of the Microsoft 365 security center?
- A. Azure Defender
- B. Azure Web Application Firewall
- C. Microsoft Cloud App Security
- D. Azure Sentinel
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender/investigate-alerts?view=o365-worldwide
NEW QUESTION # 246
You have a Microsoft 365 E5 tenant that contains the users shown in the following table.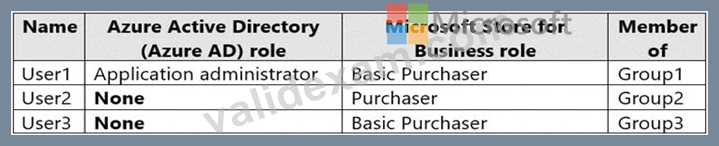
You perform the following actions:
* Provision the private store in Microsoft Store for Business.
* Add an app named App1 to the private store.
* Set Private store availability for App1 to Specific groups, and then select Group3.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.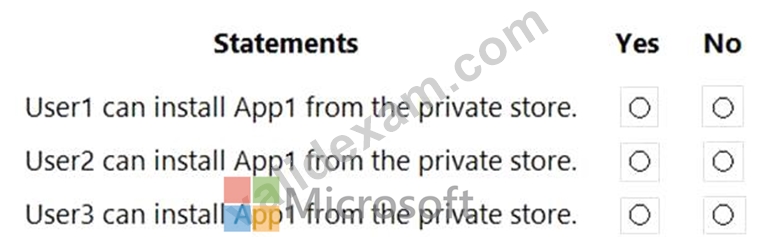
Answer:
Explanation: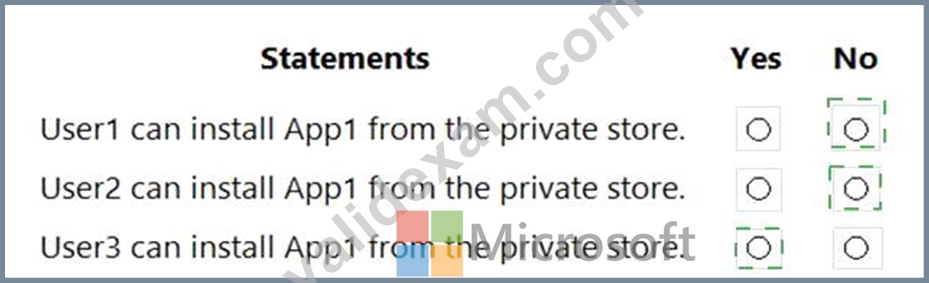
Explanation: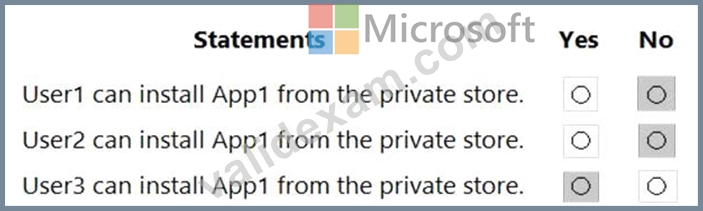
Reference:
https://docs.microsoft.com/en-us/microsoft-store/app-inventory-management-microsoft-store-for-business#priva
NEW QUESTION # 247
(You have a Microsoft 365 E5 subscription.
You are implementing Microsoft Defender for Cloud Apps.
You need to ensure that you can create OAuth app policies .
Solution: You configure Conditional Access app control .
Does this meet the goal?)
- A. No
- B. Yes
Answer: A
Explanation:
OAuth app policies are a feature of Microsoft Defender for Cloud Apps (MDCA) that allow you to:
* Monitor OAuth-connected apps
* Control app permissions
* Detect risky or overprivileged OAuth applications
Microsoft documentation clearly states that OAuth app policies are created and managed directly within Microsoft Defender for Cloud Apps , under Control # Policies # OAuth app policies .
Why Conditional Access app control does NOT meet the goal
Conditional Access app control is a different capability that:
* Integrates Microsoft Defender for Cloud Apps with Microsoft Entra Conditional Access
* Provides real-time session control for cloud apps
* Is used to control user actions (download, upload, copy, etc.) during app sessions Microsoft documentation explicitly distinguishes these features:
* Conditional Access app control is for session-based access control
* OAuth app policies are for app governance and permission monitoring
Configuring Conditional Access app control does not enable or affect the ability to create OAuth app policies .
NEW QUESTION # 248
You have a Microsoft 365 tenant.
You plan to manage incidents in the tenant by using the Microsoft Defender XDR. Which Microsoft service source will appear on the Incidents page of the Microsoft Defender portal?
- A. Azure Information Protection
- B. Azure Arc
- C. Microsoft Defender for Cloud Apps
- D. Microsoft Defender for Cloud
Answer: A
NEW QUESTION # 249
Your network contains an on-premises Active Directory domain. The domain contains 2,000 computers that run Windows 10.
You purchase a Microsoft 365 subscription.
You implement password hash synchronization and Azure AD Seamless Single Sign-On (Seamless SSO).
You need to ensure that users can use Seamless SSO from the Windows 10 computers.
What should you do?
- A. Join the computers to Azure AD.
- B. Modify the Intranet zone settings by using Group Policy.
- C. Create a conditional access policy in Azure AD.
- D. Deploy an Azure AD Connect staging server.
Answer: A
NEW QUESTION # 250
Your company has an Azure AD tenant named contoso.com that includes the users shown in the following table.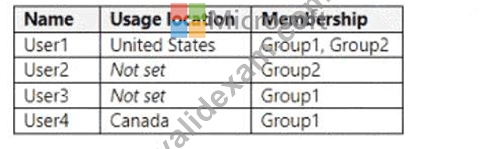
Group2isa member of Group1.
You assign an Office 365 Enterprise E3 license to Group1.
How many Office 365 E3 licenses are assigned?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: C
NEW QUESTION # 251
......
Free MS-102 Exam Files Downloaded Instantly 100% Dumps & Practice Exam: https://www.validexam.com/MS-102-latest-dumps.html
Updated Verified MS-102 dumps Q&As - 100% Pass Guaranteed: https://drive.google.com/open?id=1YQmOo_VRa5LzZ_4rTwCxNyzvyFHAfSKU